A maintenance laptop boards
A device attempts access outside its authorised scope. The event is flagged for review and the connection can be isolated according to the agreed operating procedure.
MDM-PROTECT is an onboard protective layer for inland vessels, powered by aXite and monitored from shore. It separates the connected IT environment from the operational systems that keep a vessel moving.
Talk to a maritime OT-security expertNavigation, engine management, communications and maintenance devices increasingly share a connected environment. That makes the boundary between administration and operation a practical security question for shipowners, charterers and logistics partners.
MDM-PROTECT addresses that boundary on board. It does not replace vessel operations or shore-side responsibility; it adds a scoped protective layer and an evidence trail around the systems in scope.
A vessel's cyber event can affect schedules, cargo handoffs and the partners that depend on the route. MDM-PROTECT keeps the operational boundary visible while the vessel is underway.
On board
A compact hardware unit between IT and OT.
From shore
Monitoring, review and reporting coordinated with the operator.
MDM-PROTECT is an onboard unit plus a managed service, installed and configured around the vessel's existing connections. It sits between the IT environment (internet, communication and administration) and the OT environment (navigation, engine management and operational controls).
MDM is the maritime service and monitoring partner. aXite provides the underlying field-level protection technology. The exact vessel boundary, escalation path and responsibilities are agreed during implementation.
Discuss MDM-PROTECT01 /
The onboard unit is installed and configured around the vessel's existing IT and OT connections during an agreed installation window. Each installation is scoped to the vessel.
02 /
The unit monitors traffic between the connected IT environment and the operational systems that keep the vessel moving.
03 /
The unit detects events and applies agreed local policy blocking. The shore team assesses events 24/7 and coordinates notification and response with the operator.
04 /
Monthly shareable fleet reports give operators and chain partners a documented view of network activity, anomalies and agreed actions.
A device attempts access outside its authorised scope. The event is flagged for review and the connection can be isolated according to the agreed operating procedure.
An update from an unverified source is treated as an event requiring review before it reaches an operational system.
Unexpected external communication is detected against the vessel's established traffic patterns and recorded for investigation.
Monitoring continues, connections are logged and the reporting trail is maintained while the vessel operates.
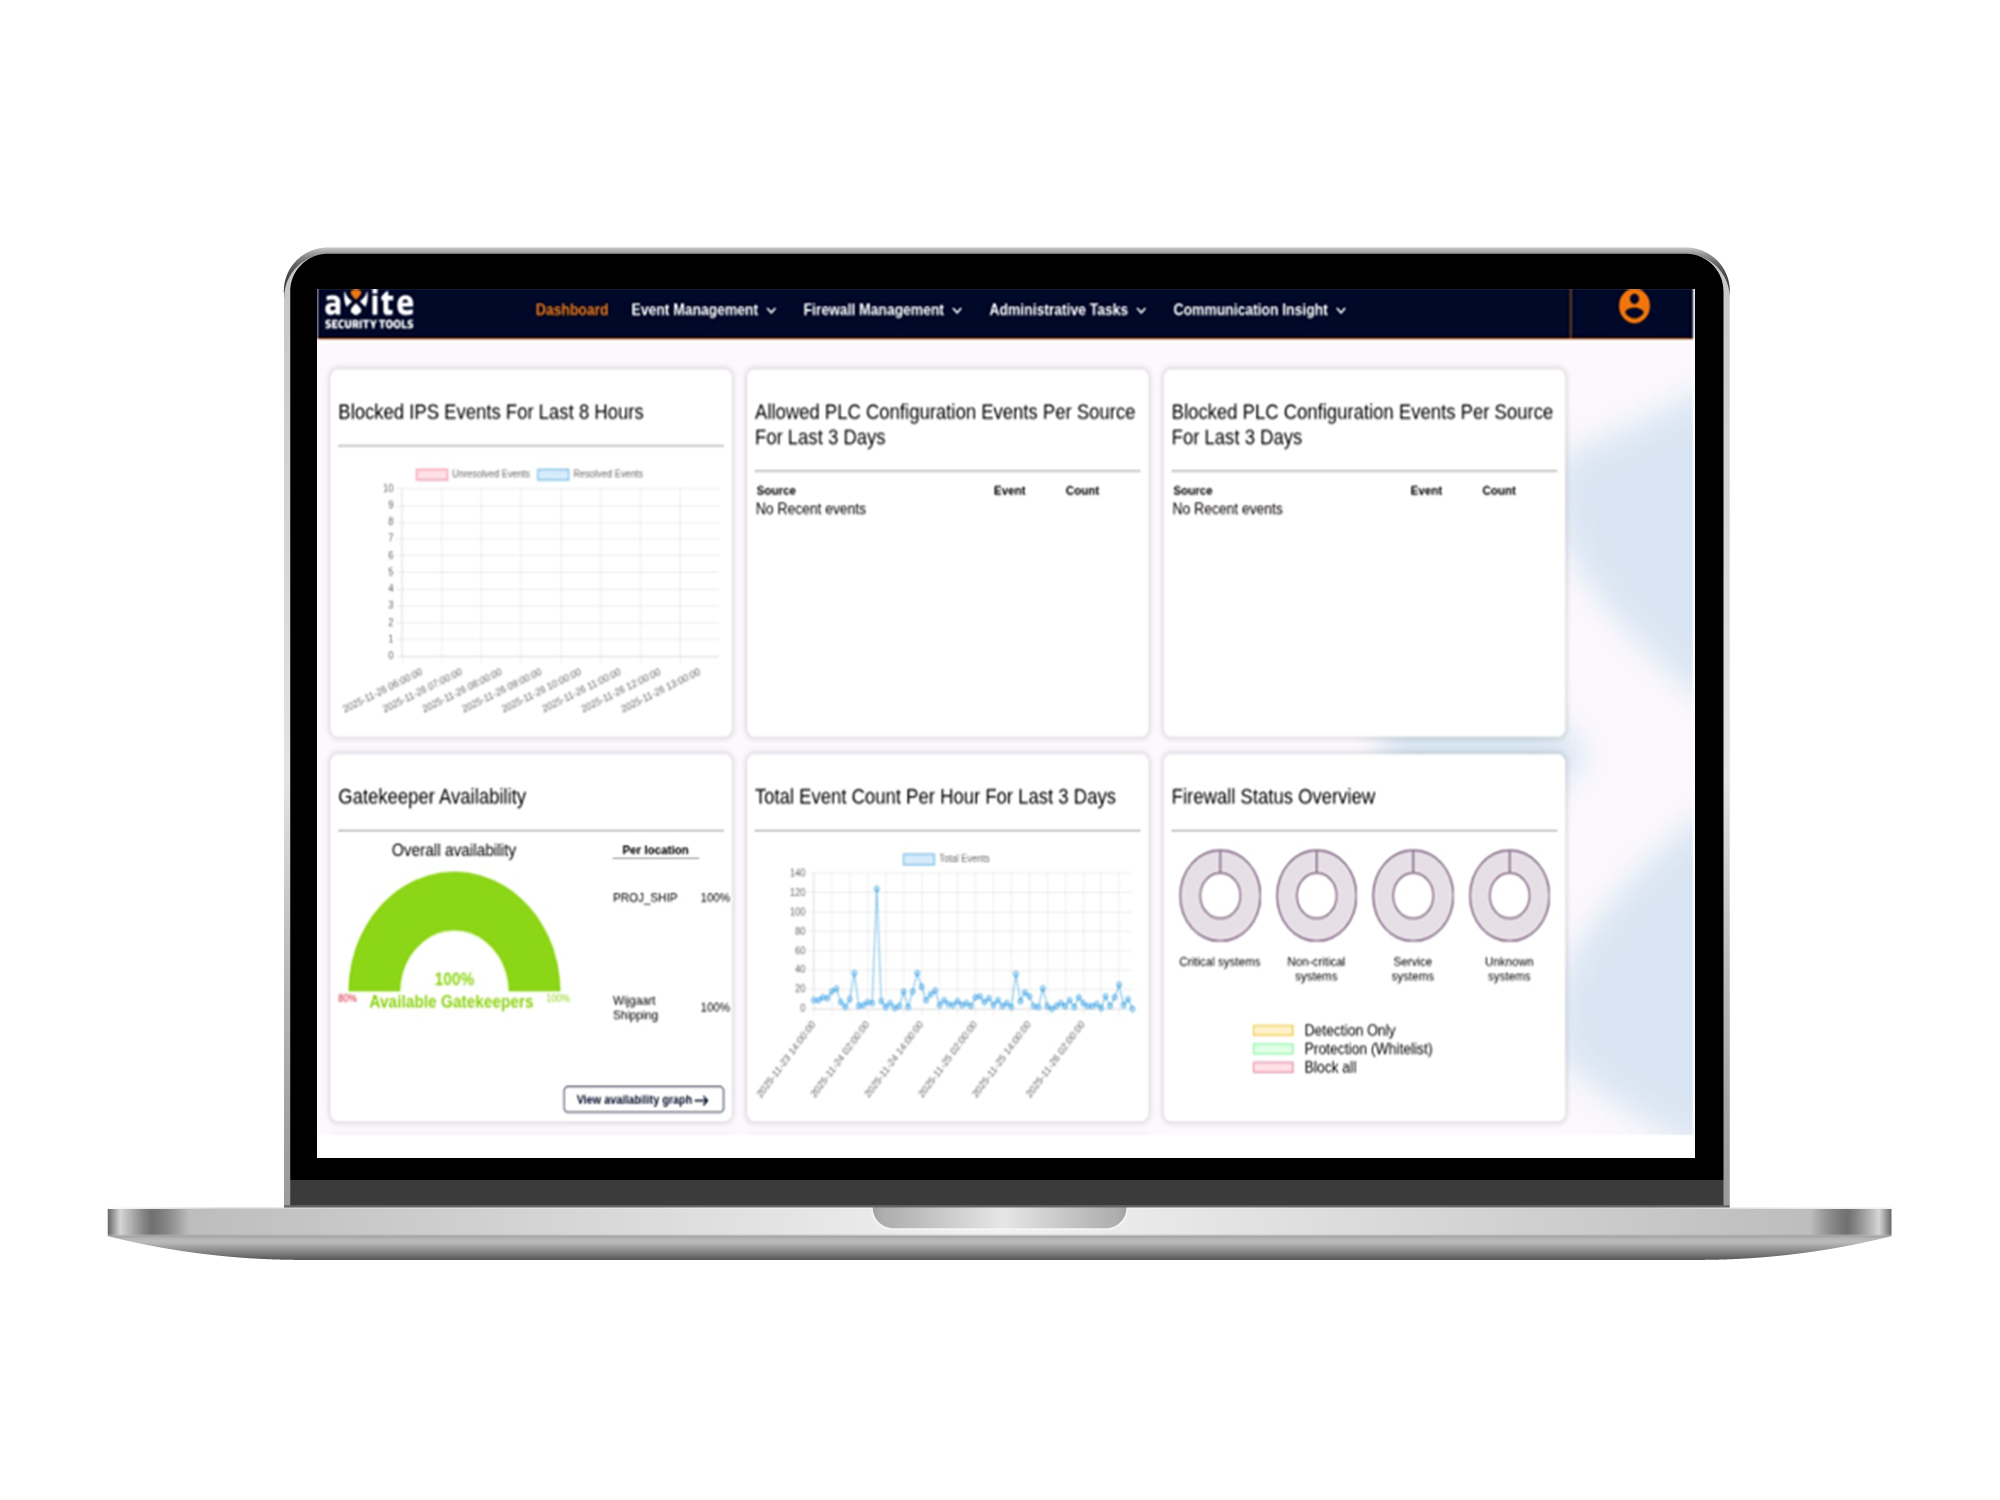
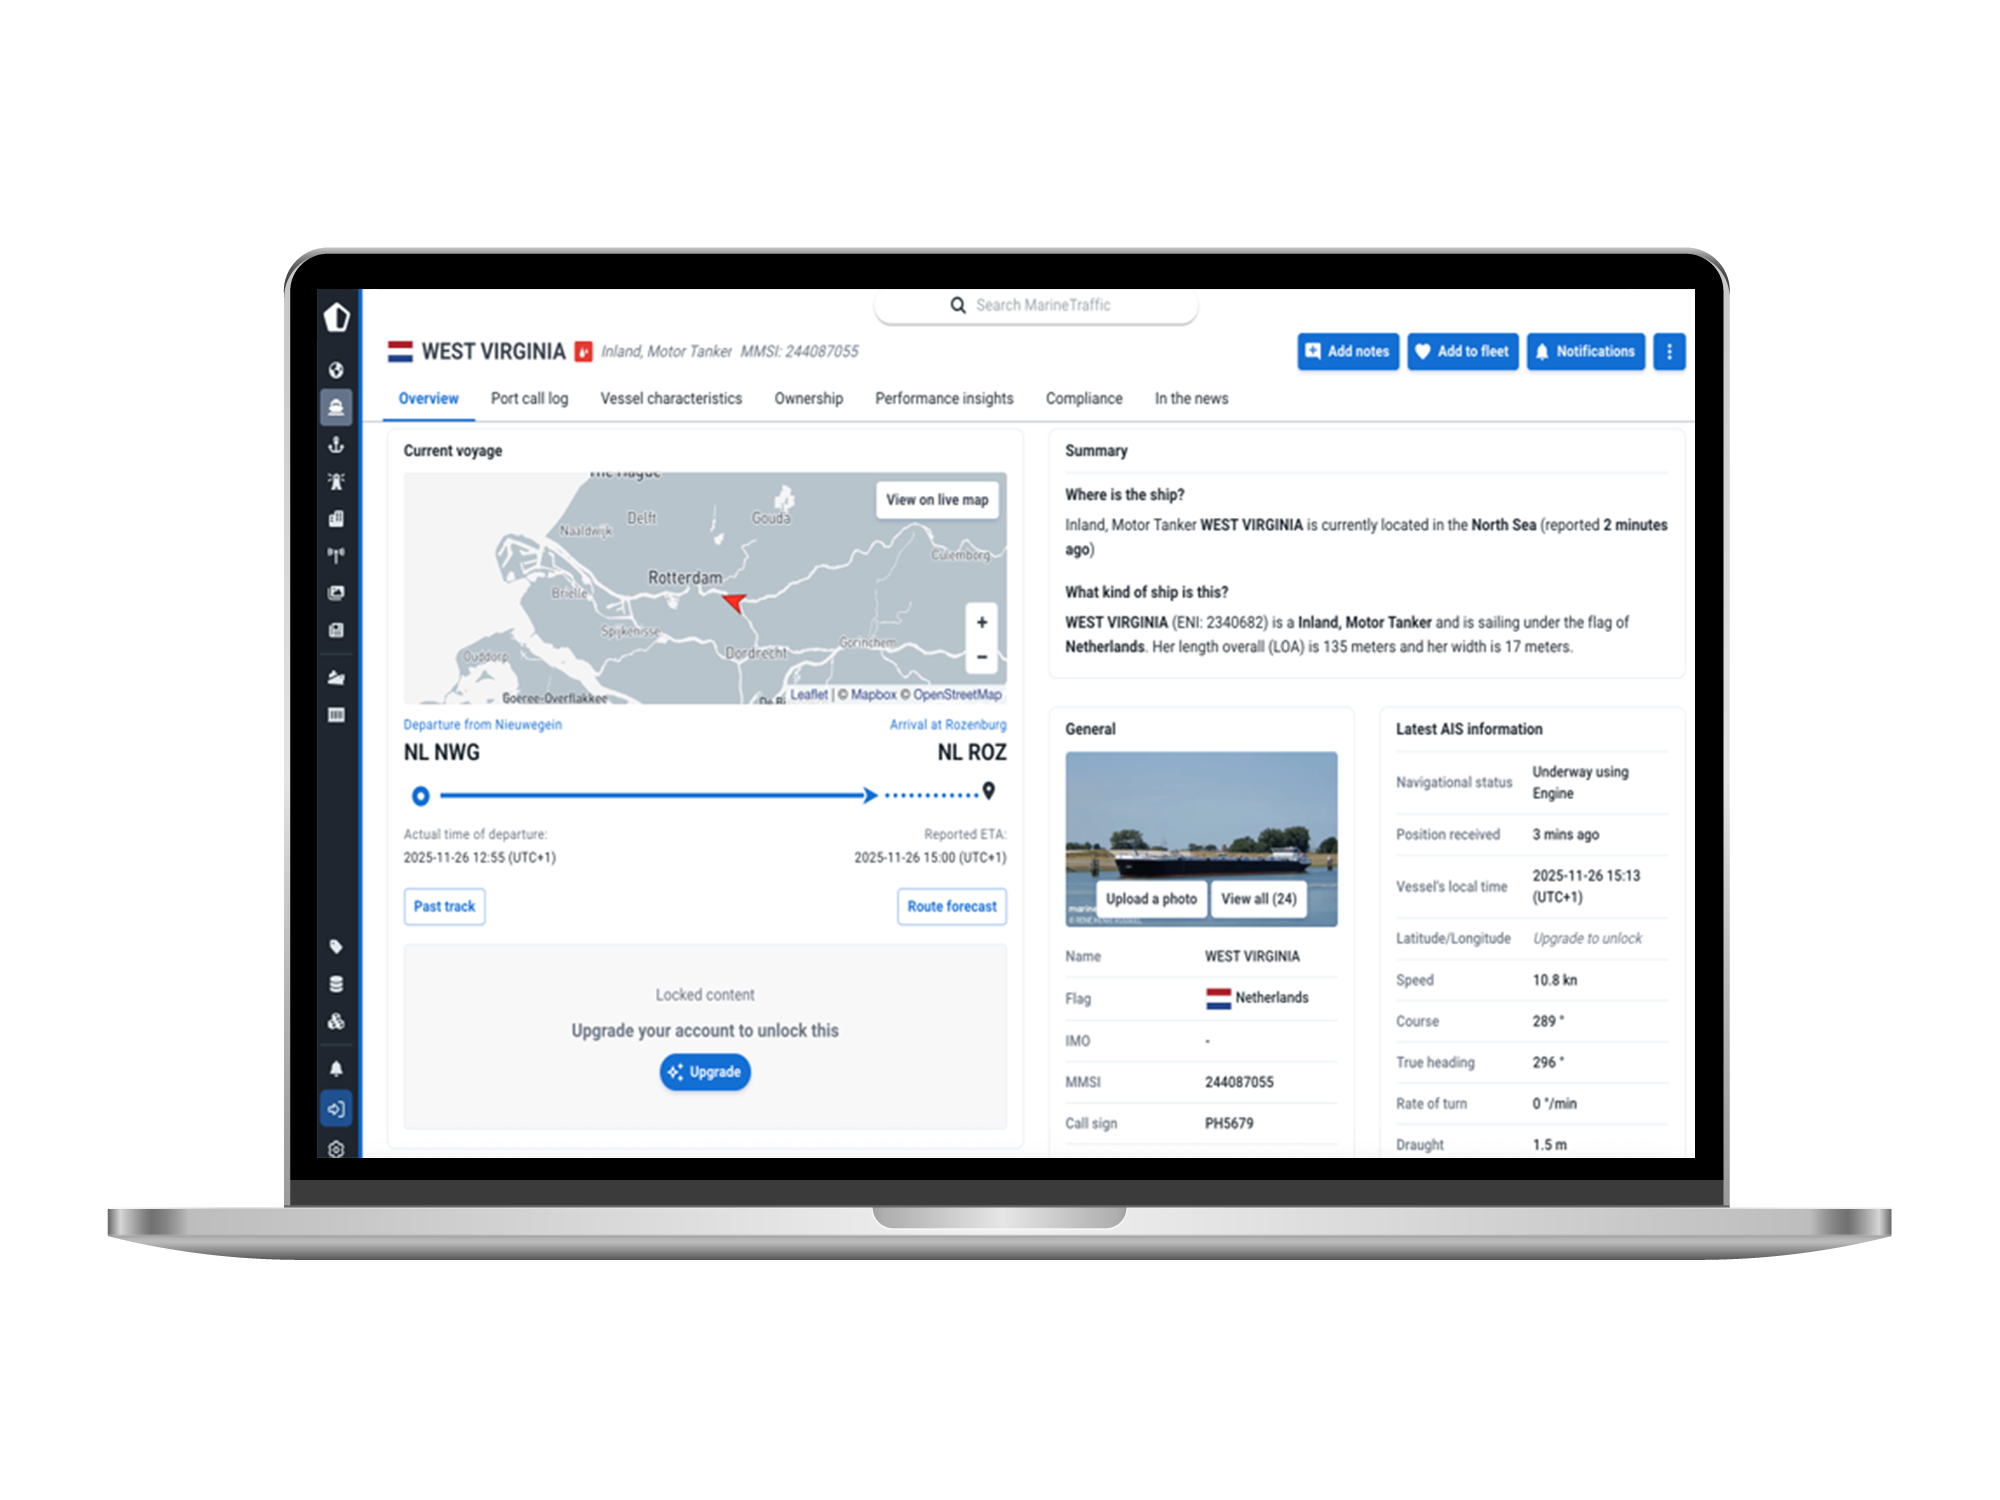
Shipowners and operators, cargo owners, charterers and fleet managers each carry different responsibilities. MDM-PROTECT supports the assessment, monitoring, incident documentation and reporting conversations that those responsibilities require.
It can support the demonstrable filling-in of relevant controls; it does not make an organisation independently compliant. Applicability and customer responsibilities must be assessed for the specific vessel and chain.
MDM-PROTECT was developed, tested and refined on MTS West Virginia with Wijgaart Shipping, its development partner and first customer, and Shipping Technology as technical partner. Installation, data flows, retention, responsibilities and escalation are agreed for each service.
Discuss the maritime protection boundary