Experience the attack. Understand the impact. Protect your live OT operations.
AX-Cyberrange brings a Digital Twin, AI-guided pentesting and process modelling into one on-premises test environment. Investigate what an attack would do, without experimenting on live operations.
A platform for defence and government organisations with mission-critical OT.
Request a live demoAX-Cyberrange.
From cyber event to process effect.
When a pentest leaves the process question unanswered.
A vulnerability or system change can raise questions that cannot be safely investigated on live OT. AX-Cyberrange is a platform for testing agreed attack scenarios against a representative copy, and examining the modelled process effect and what the defences observe.
Think of a flight simulator for operational cyber resilience, built around a defined environment, not a generic exercise. The test scope establishes which assets and behaviours need to be represented.
See how the isolated copy worksWhat is a cyberrange?
A cyberrange is a controlled environment where teams recreate digital systems, run attack and defence scenarios, and test how people and technology respond, without running those exercises on live operations. It can support training, technology testing, validation and experimentation. The systems and scenarios are chosen around the question to be investigated.
What makes a cyberrange different for OT?
In operational technology, a cyber event can affect a physical process. An OT range therefore needs more than computers and a network: it needs to represent the relevant controllers, control logic and process behaviour. How closely it represents reality determines what a test can tell you.
How is that different from a pentest?
A pentest is an assessment; a cyberrange is an environment in which testing can take place. A range can support pentesting, team exercises and repeated checks after a change. Its value depends on the systems it represents and the questions the test is designed to answer.
An attack path is only
part of the answer.
AX-Cyberrange brings the attack scenario, the modelled process effect and defence observations into the same test environment.
Connect the attack path to the process
A scanner can identify known weaknesses. It does not, by itself, establish the physical effect of exploiting them in a particular installation.
AX-Cyberrange combines AI-guided pentesting with an OT copy and process modelling to investigate executable paths and their modelled operational consequences.
Test the environment that matters to you
A generic training range can develop skills without representing the configuration and control behaviour of your own environment.
The test environment is built around agreed assets, controllers, firmware and process behaviour. Supported systems and model limits are established before interpreting the findings.
Bring attack and defence into the same test
A finding is a starting point. Teams also need to investigate whether their defences see the scenario and what changes after remediation.
Compare process effects with the signals observed by the defences. Repeat an agreed scenario after changes to the copy, with agents and data on customer-controlled infrastructure.
Shared vocabulary
Describing a scenario with MITRE ATT&CK for ICS
MITRE ATT&CK is a public knowledge base of adversary tactics and techniques that have been observed in real attacks. Its ICS matrix covers industrial control systems, which gives teams a common language to discuss a scenario. It is not a product certification or endorsement, and this selection does not map the full coverage of AX-Cyberrange.
Open the MITRE ATT&CK for ICS matrix (opens in a new tab)Initial Access
External Remote Services
Adversaries may use remote access services that are reachable from outside networks to gain a foothold in the environment.
T0822 on attack.mitre.org (opens in a new tab)Execution
Change Operating Mode
Adversaries may switch a controller between operating modes, which changes how it accepts logic and commands.
T0858 on attack.mitre.org (opens in a new tab)Impair Process Control
Modify Parameter
Adversaries may alter the parameters a controller works with, changing how the physical process behaves.
T0836 on attack.mitre.org (opens in a new tab)Impact
Loss of Availability
Adversaries may disrupt the systems and processes that operations rely on, so they are no longer available.
T0826 on attack.mitre.org (opens in a new tab)
An illustrative selection of four techniques, not the full matrix.
The working loop 04 / 07
Runtheattackagainstthecopy.
Never against production.
Live operation
The reference. Not the test target.
Isolated test copy
Control logic, network and process model.
A scenario targets the copied control system. The process model shows the consequence; monitoring shows what the defences observed.
Conceptual illustration, not a product screen or test result. The agreed test scope defines the supported systems and model fidelity.
From attack path to retest
- 01
Replicate
Define the systems and process behaviour the isolated copy needs to represent.
- 02
Investigate
Run an agreed attack scenario with AI-guided pentesting agents inside that boundary.
- 03
Observe
Look at the process effect and what the defences detected or missed.
- 04
Retest
Change the copy or its controls, then repeat the scenario and compare findings.
The platform is the starting point.
Your OT defines the test environment.
A platform, shaped around a customer-specific test environment. Assets, scenarios and model fidelity are agreed for each environment.
Platform core
Pentesting agents, test orchestration, dashboards and reporting form the platform core. These capabilities are being developed and validated within the platform.
Your test environment
The copy represents the agreed network, controllers, firmware and process behaviour. It can use representative hardware, emulation and process models, with supported systems and model limits defined upfront.
Define the first end-to-end test.
Agree the assets, attack scenario, process and defence observations to review, and the conditions for a retest. The test environment requires system specifications, representative systems and a customer-approved isolation and information-import design. Classification, update and accreditation requirements are established for each environment.
Findings apply within the copy’s model limits. No AX-Box Gatekeeper or Interlock purchase is required.
In practice 06 / 07
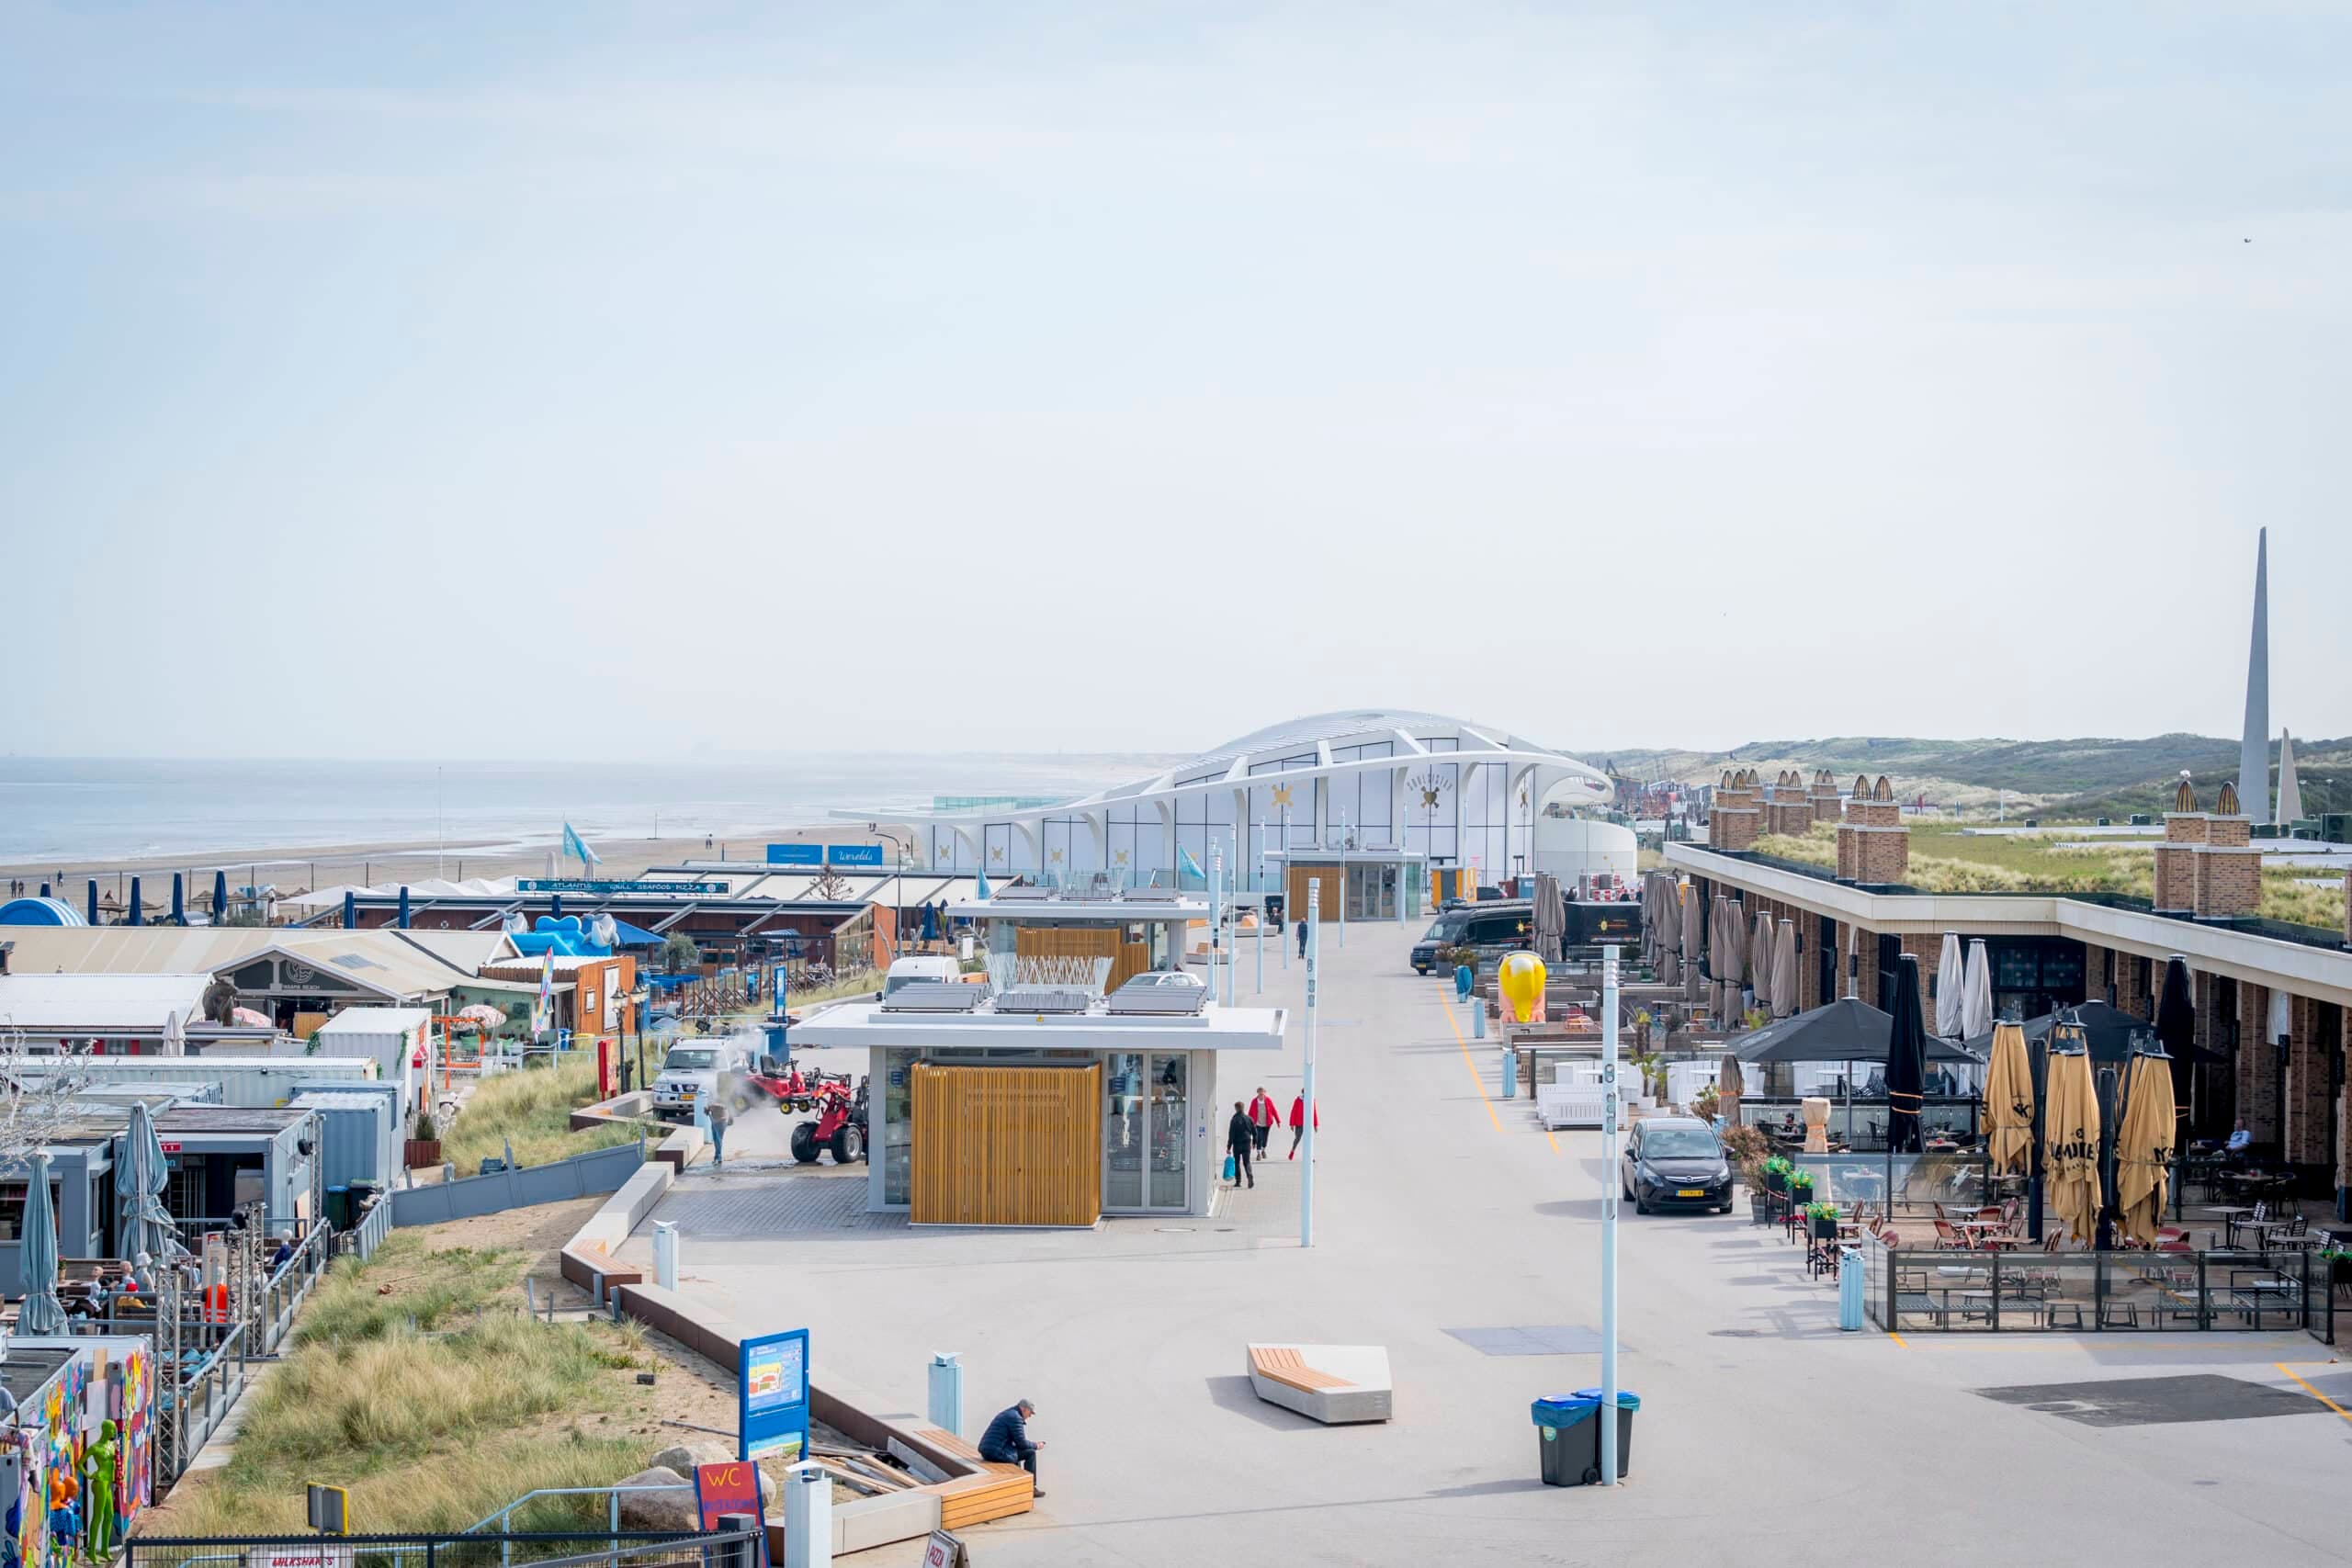
Digital twinning at Slim Strandnet
In Scheveningen, aXite is creating a digital twin of the Slim Strandnet for the Cyber-Secure Energy Hubs project, co-funded by the European Union and Kansen voor West. Project in progress.
Start with one environment and one test question.
Bring the assets, scenario and process consequence you want to investigate. Together we define the copy boundary, prerequisites and how the findings will be reviewed.