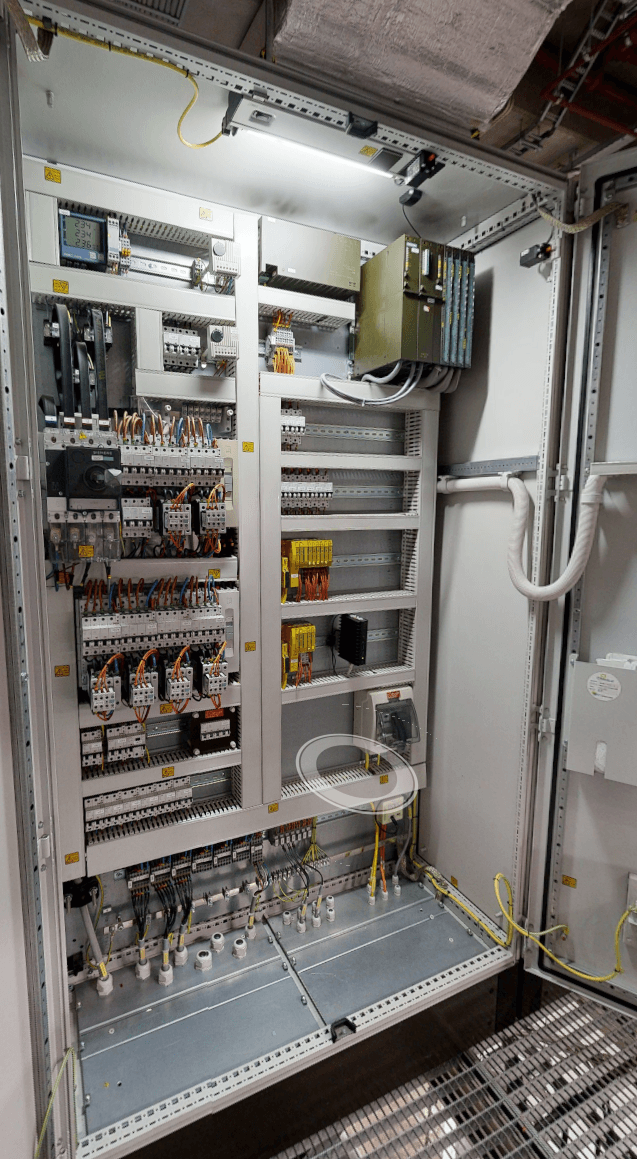
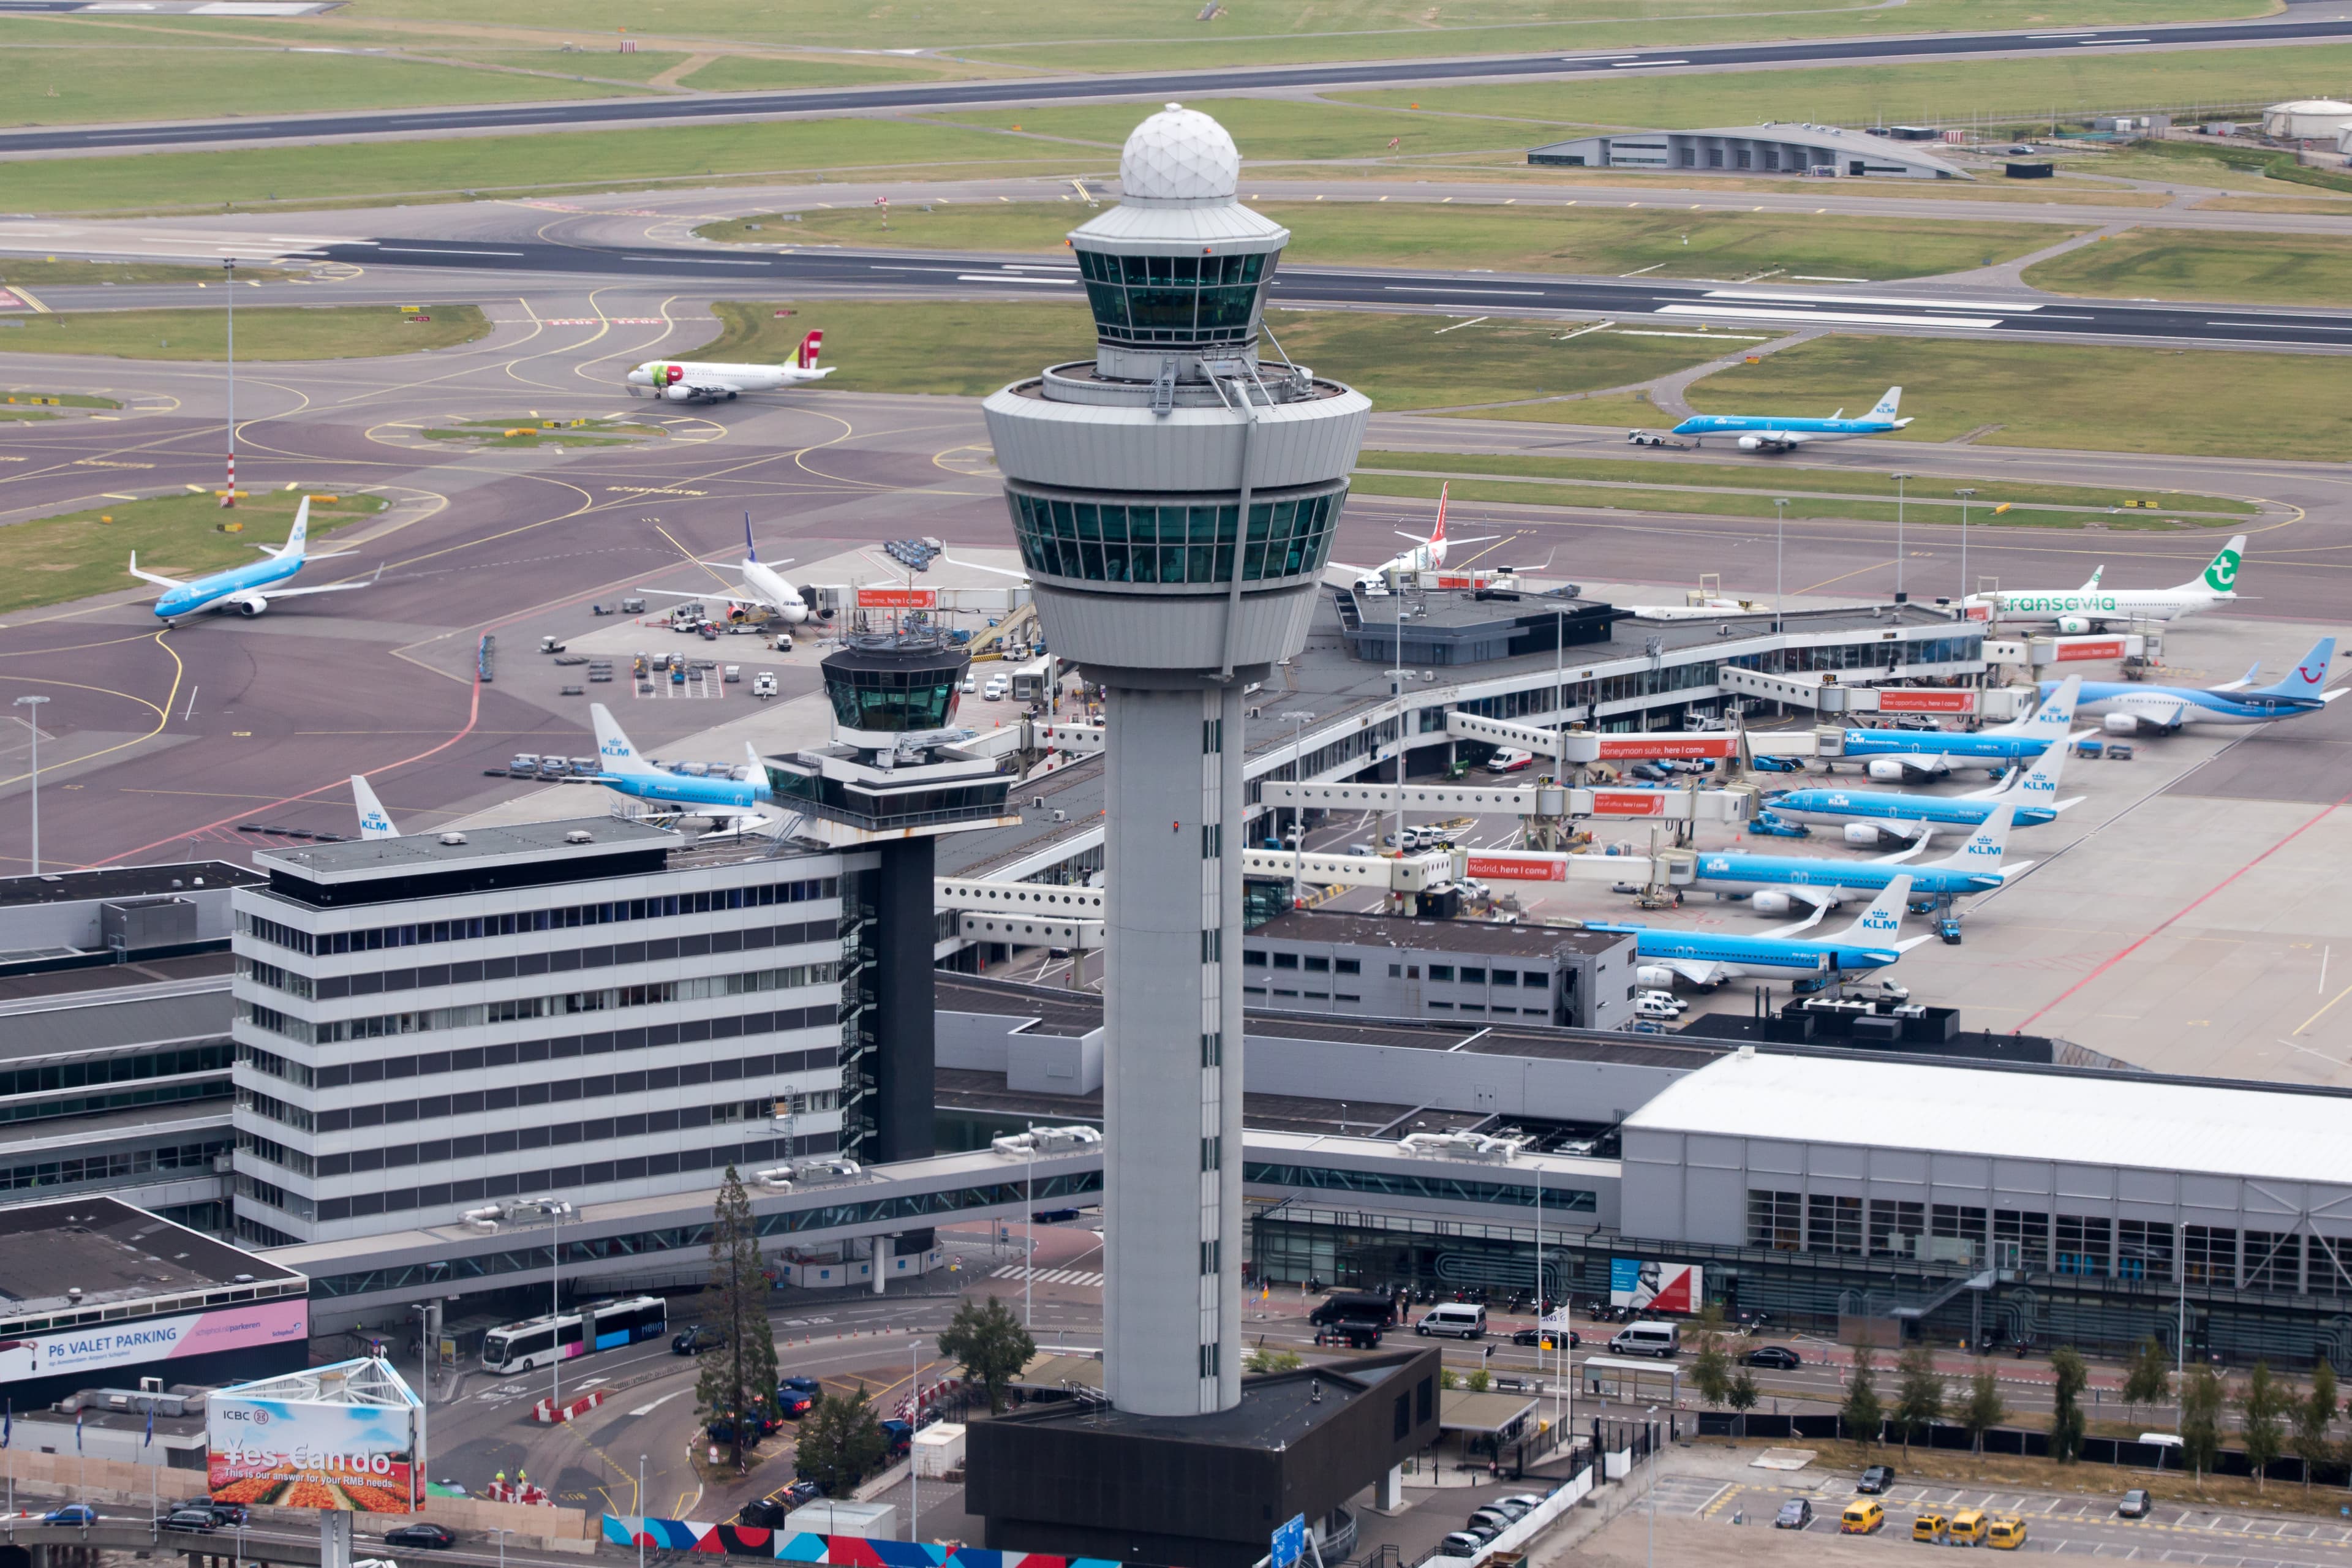
Schiphol
AX-Box Gatekeeper in baggage operations.
AX-Box Gatekeeper has protected legacy baggage-system PLCs at Schiphol since 2017.
Read the Schiphol caseProtect adds local cybersecurity controls around critical operational assets. Authorise access, govern communication and record relevant events, with the deployment matched to your systems and operating requirements.
Maintenance, suppliers and operational systems need to reach equipment that must stay in service.
Legacy controllers and newly connected devices do not always provide the required security for access, communication and management. Protect adds these security controls at the supported asset boundary to help keep the installation safe.
Monitoring can identify suspicious activity; segmentation limits network reach. Protect complements these controls by enforcing agreed permissions and communication rules at the supported asset boundary.
The protection boundary
A connection to an asset is not permission to change it.
Apply the controls your operation needs. Supported protocols, configuration checks and event coverage are established for each deployment.
Give operators, maintenance teams and suppliers authorised access to the assets they need. Set permissions and access windows around the installation, rather than relying on network reachability alone.
Mediate supported protocols and permitted operations at the asset boundary. Apply local policies to restrict unwanted communication while allowing the agreed operational traffic.
Check supported configuration and change activity against the agreed baseline. Make unexpected changes visible for investigation, without treating every maintenance action as an incident.
Record relevant access, communication and security events. Give operators evidence to review what happened, investigate deviations and demonstrate how controls are applied.
One local protection principle, applied differently. Choose your environment to see the assets, product and delivery model that fit.
01
AX-Box Gatekeeper
Add controls around legacy PLCs in airport operations. Govern maintenance access, communication and changes without modifying PLC firmware or code.
Explore Protect for airports
02
MDM-PROTECT
Protect operational systems on board commercial inland fleets. MDM combines local IT/OT protection with monitoring from shore, powered by aXite.
Explore Protect for inland shipping
03
AX-Energy Protect
Add local detection and enforcement around smart meters and controllable energy grid endpoints. Assess the supported installation and validate lifecycle requirements before scaling.
Explore Protect for energy
04
AX-Box Gatekeeper
Protect controllers in high-criticality steel processes, pipelines and terminals. Define the supported access, protocol and change controls around the existing installation.
Explore Protect for critical industryProtect connects asset-level controls to the people responsible for the operation. Communication and event reporting have different roles.
Communication path
Operational systems, operators and service partners request access or exchange data.
The configured protection layer checks supported communication and applies the agreed permissions and policies.
Permitted communication reaches the protected controller or device within the supported deployment scope.
AX-Manage is the on-premises platform for managing AX-Box Gatekeeper units. It records the protected controllers, their configuration and approved changes, and shows events from controlled PLCs in a timeline, so operators can review what happened at each controller. Monitoring is provided by aXite. An API for sharing data with your own SOC is planned but is not yet available. Monitoring responsibilities, connectivity and data flows are defined per deployment.
AX-Box Gatekeeper provides the local protection technology for the PLC-based offers.
The vendor-independent AX-Box Gatekeeper adds controls without modifying PLC firmware or code on supported controllers and protocols. Installation is planned with the operator in a maintenance window; protocol compatibility, operating behaviour and acceptance are validated for the site.
Explore AX-Box Gatekeeper technology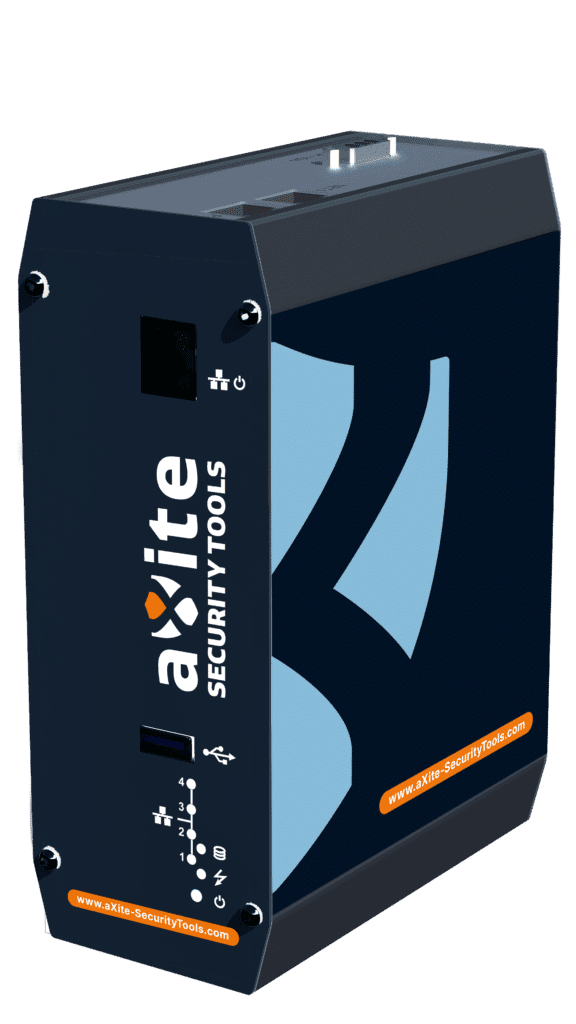
Operational use and approval for application answer different questions. These examples relate to the named products and environments.
Schiphol
AX-Box Gatekeeper has protected legacy baggage-system PLCs at Schiphol since 2017.
Read the Schiphol case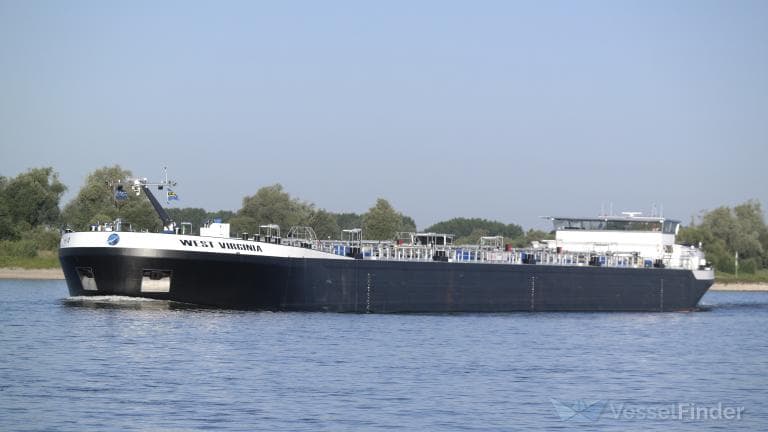
MTS West Virginia
Onboard protection and monitoring from shore for Wijgaart Shipping, delivered by MDM and powered by aXite.
Read the vessel case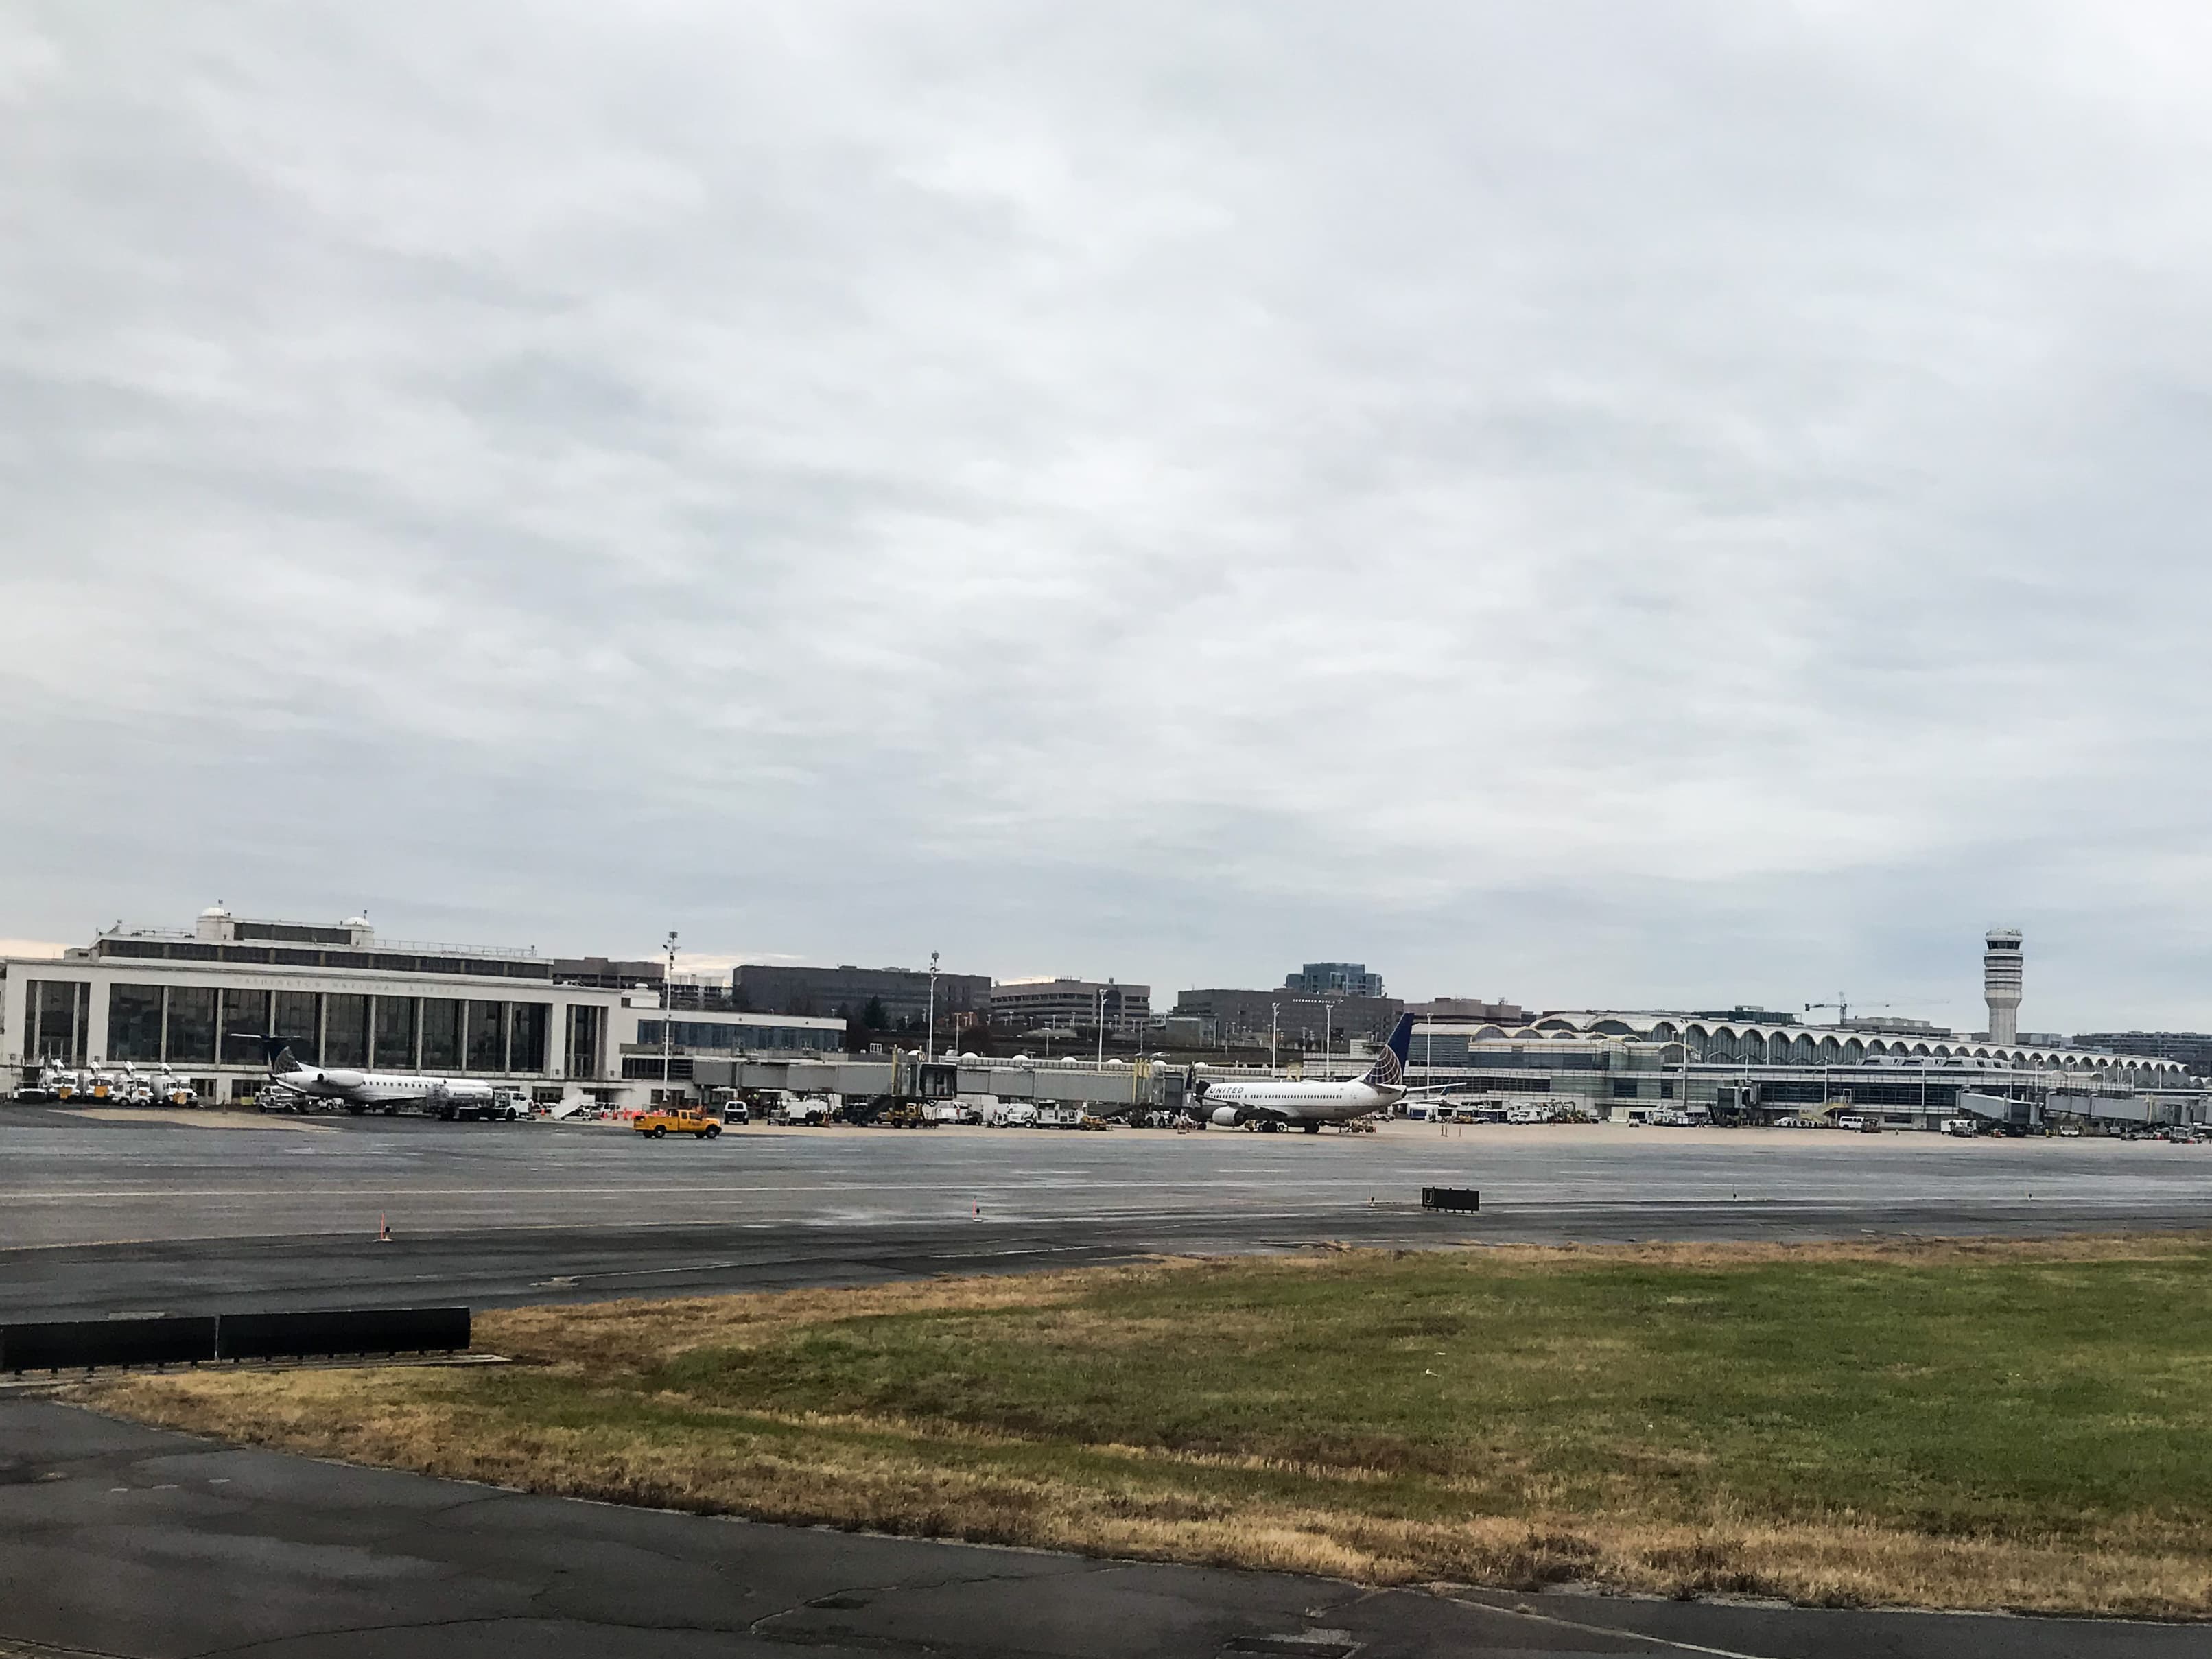
TSA
TSA approval covers AX-Box Gatekeeper application. It is not a count of operational deployments.
Approval for application · Airports
Bring your assets, protocols, maintenance access and existing controls. Together we can identify the right Protect application and establish installation and acceptance requirements with the responsible operators.